

Aikido
Aikido Security is a European application and cloud security platform that finds, prioritizes, and fixes vulnerabilities across code, dependencies, containers, cloud infrastructure, and runtime. It replaces a stack of separate scanners with one platform that developers actually use, and it feeds its findings straight into Kertos as audit evidence.
Security built for the teams who ship the code
Headquartered in Belgium, Aikido Security builds a developer-first security platform used by engineering teams across Europe and beyond. Aikido is certified to ISO 27001:2022 and SOC 2 Type II.
What this partnership delivers
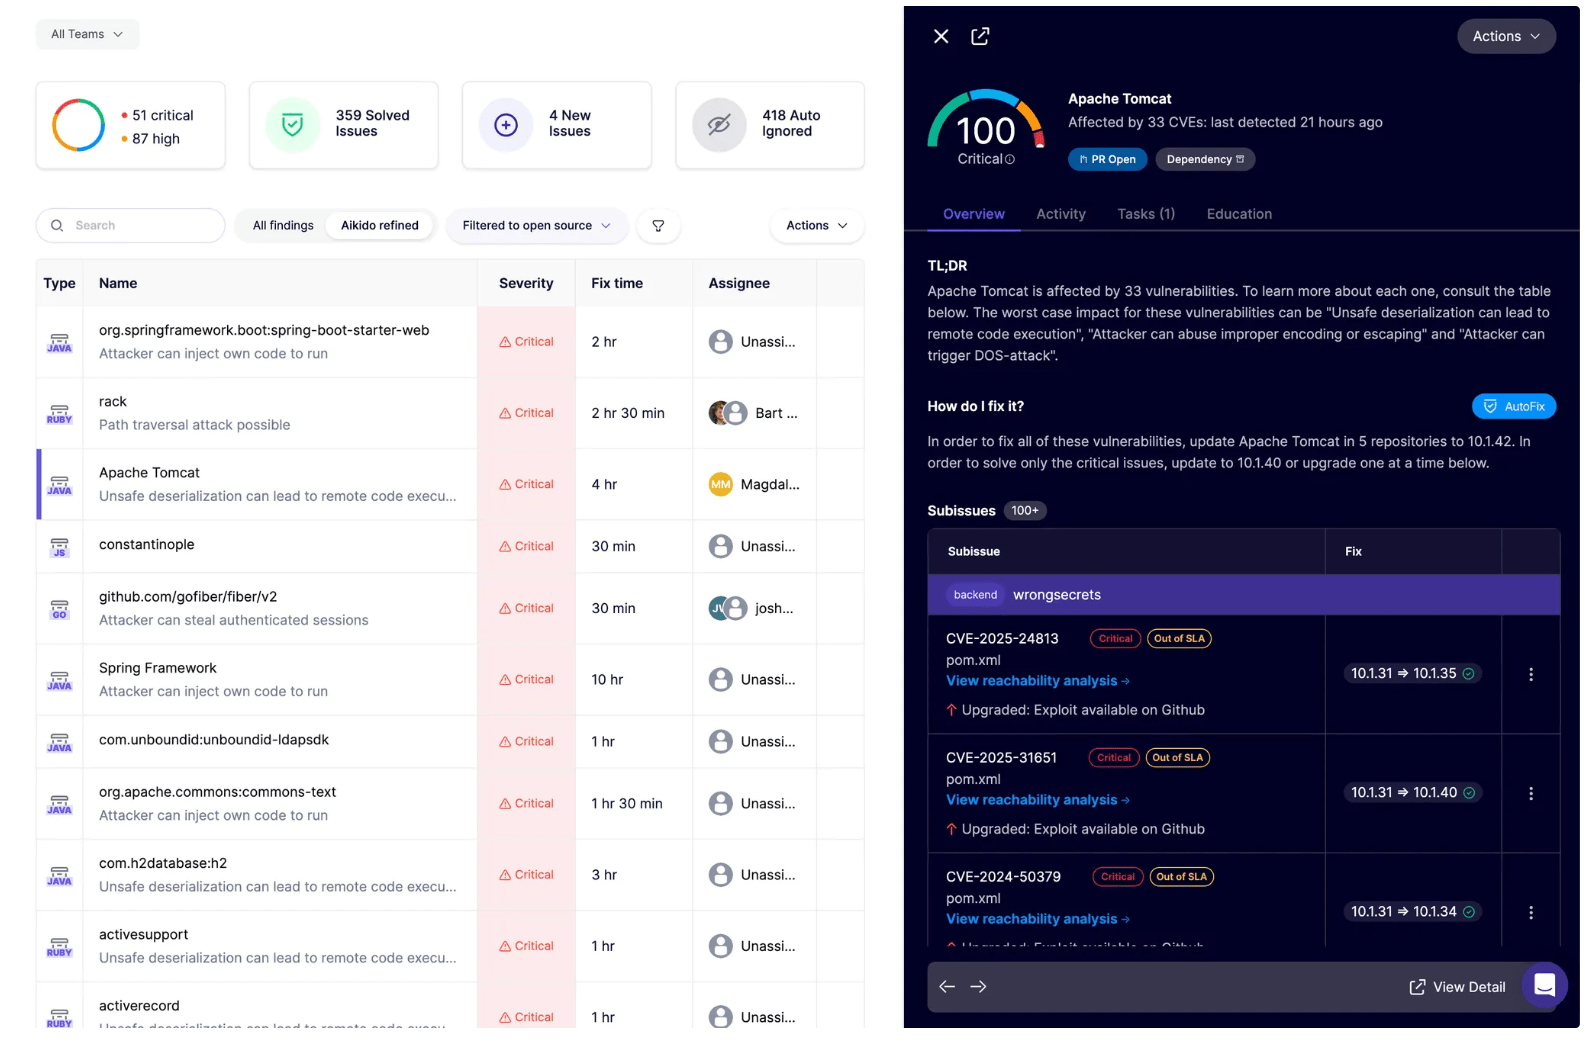
Kertos reads your Aikido vulnerability findings and the remediation deadlines your team has set.
Kertos tracks which findings were closed on time and files the result as audit evidence.
Covers controls for vulnerability management, secure development, and security testing.
Set up once, then refreshed every day in the background or on demand, read-only.
Our Partnership
Services and how Aikido works with Kertos
What Aikido covers. Aikido consolidates more than 15 security scanners into a single platform. Code security includes SCA for open source dependencies, SAST, secrets detection, malware detection, SBOM generation, and container image scanning. Cloud security covers CSPM, infrastructure as code scanning, virtual machine scanning, and data posture. On the offensive side, Aikido runs DAST, API scanning, attack surface monitoring, and continuous pentesting. Runtime protection closes the loop in production.
Why engineering teams pick it. Aikido triages findings against the context of your codebase and can open one-click pull requests to remediate. Its SAST engine alone cuts false positives by 85%, which keeps developer attention on the findings that are genuinely exploitable. Scanning happens where the work happens, in the repository and the pipeline, not in a separate portal that nobody opens.
How the integration with Kertos works. Connecting Aikido to the Kertos platform takes one connection. From then on, Kertos pulls your Aikido findings and the remediation deadlines you have set, read-only, refreshing once a day in the background or on demand. Kertos tracks whether findings are resolved inside those deadlines and turns that record into audit evidence automatically.
What that evidence proves. The synced data supports vulnerability management, secure development, and security testing controls for ISO 27001, the security testing and vulnerability management requirements under SOC 2, and the NIS2 obligation to demonstrate that security weaknesses are identified and remediated. Your evidence comes into being where the work happens, instead of being assembled from screenshots three weeks before the audit.
What stays your job. The integration documents your vulnerability management, it does not do it for you. Your team still sets sensible remediation deadlines and fixes what the scanners surface. Kertos certified experts review the evidence with you, flag gaps before an auditor does, and prepare the control narrative around it.
Two European vendors, one workflow. Aikido handles security in Belgium, Kertos handles compliance in Germany. Both operate under European law on European infrastructure, so security scanning and compliance evidence stay inside the EU.
