An external CISO for your ISMS

Kertos gives you an external information security officer (CISO): they support the ongoing development of your ISMS, advise your management, and prepare you for upcoming audits. And they work where your risks, measures, and evidence already live — in the Kertos platform.

Any Bill
Blacklane
Contract Hero
Enpal
Flink
McMakler
Personio

<h2>An external CISO who already knows your ISMS</h2>

‍

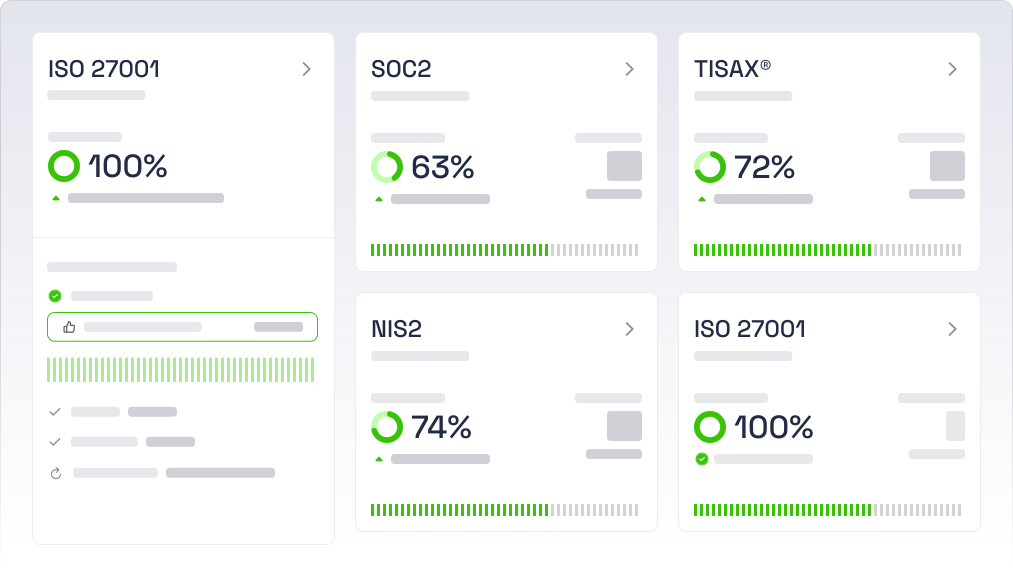
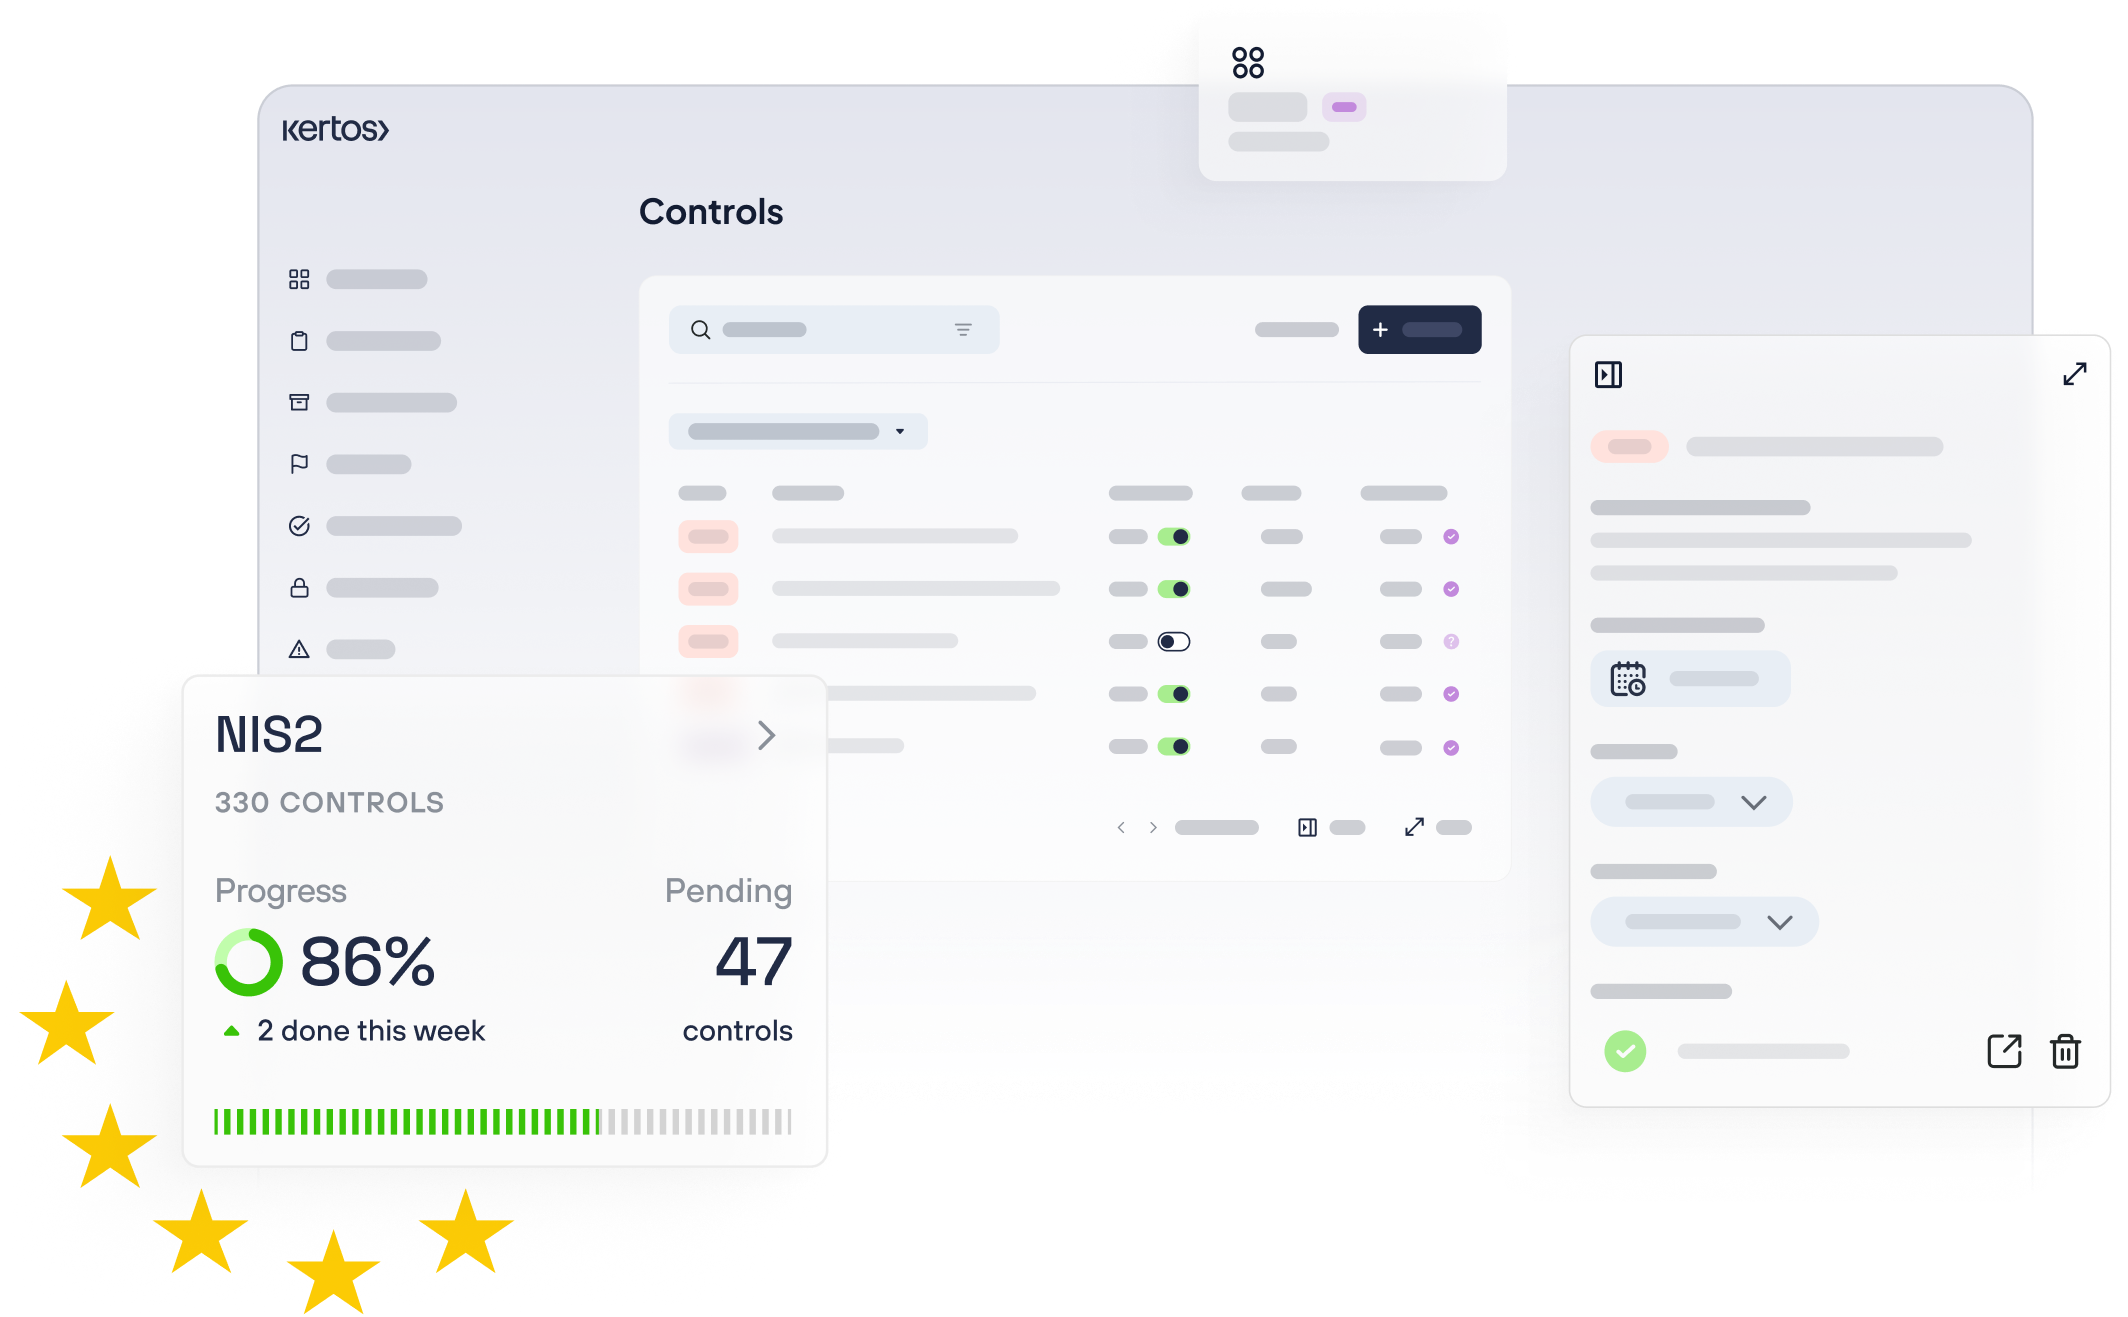
Your external CISO has an up-to-date view of risks, measures, documents, and training status in the Kertos platform at any time. That removes the routine of gathering paperwork and re-explaining where things stand at every catch-up. Before the engagement starts, we introduce you to your external CISO, and you can of course request evidence of their qualifications.

100%

audit pass rate

98 %

customer satisfaction

>500

clients managed

>10

served industries

No items found.
Featured Image

C00

Running and improving your ISMS

Your external CISO supports you continuously in managing your information security. They help identify and assess risks, recommend suitable measures, and support their implementation and effectiveness review. They also advise on the regular management review and prepare the relevant information with you. Decisions on risks, measures, and approvals always stay with you.

Expert assessment of your risk assessment and security objectives

Preparation and facilitation of the management review

Review of ISMS documentation and evaluation of measure status

Featured Image

C00

Audits and Reports

Ahead of an audit, your external CISO supports the preparation, reviews the relevant evidence, and points out visible gaps or open actions. After the audit, they help put the findings in context and derive suitable corrective action. On request, they accompany audits and are available for expert questions on the ISMS. For security incidents, they support the assessment and help derive sensible improvement measures. Your management receives a regular, concise overview of ISMS status, material risks, and what needs attention.

Preparation and follow-up for internal and external audits, with attendance on request

Expert assessment of security incidents and vendor questions

Regular reporting on status, risks, and open actions

TESTIMONIALS

What Our Customers Say

Compliance that convinces: whether B2C, B2B, startup, or scaleup, Kertos fits companies with growing compliance requirements.

Dr. Lukas Pfahlsberger
Co-Founder & CEO
No items found.

"Compliance as a Competitive Advantage"

Using Kertos is a major advantage for us in the sales process because it allows us to be faster. Critical questions regarding IT security, compliance, and GDPR are essentially pre-empted by referring to our Kertos Trust Center. This boost in customer confidence has paid dividends so far.

‍

Thomas Gan
Thomas Gan
Co-Founder, MuffinTech

“Fast, straightforward, and seamlessly automated!”

It's incredible how effortlessly the Kertos team guided us through the complex ISO 27001 process. Fast, straightforward, and seamlessly automated! Compliance is no longer on our minds because Kertos takes care of everything.

Matthias Knoche
Matthias Knoche
COO, McMakler

“European compliance automation built for mid-market teams”

As a mid-market company, we don't have a large compliance team, and Kertos means we don't need to build one. It automated our GDPR workflows so thoroughly that work which used to take days now takes minutes, and in many cases doesn't need a compliance manager to touch it at all. Onboarding took an afternoon, including connecting our own homegrown software via API. And unlike the mass compliance providers, we get a European partner who understands our requirements firsthand.

Stefan Hessel
Stefan Hessel
Salary Partner & Head of Digital Business, reuschlaw

“Reliable partner for all compliance issues”

For us, Kertos is the reliable partner for all compliance issues. Whether it's ISO27001 certification or data protection, we really appreciate Kertos' expertise and support.

Herwig Gangl
Herwig Gangl
Co-Founder

"Implementing data protection and compliance in a structured way with Kertos"

From the very start, we felt that we were working with a partner who takes a realistic view of the effort and the process involved. The result, for us, is now a central platform that lets us manage our compliance topics in a structured way, across teams.

Claudio Kusnitzoff
Claudio Kusnitzoff
Teamlead Online Product, Wellster Healthtech

“Reclaim valuable time”

With Kertos' access management solution, we can efficiently automate the tracking and documentation of access to our protected systems. This gives us valuable time that we can invest in developing our own product.

<h2>Information security, professionally supported — with an external CISO.</h2>

‍

CTA Image
Resources

Discover Our Resources

Find useful whitepapers, videos, and practical tools to help you efficiently achieve your compliance goals.

No items found.
FAQ

Frequently Asked Questions

Information about Kertos' compliance platform

How does an external CISO differ from a virtual CISO (vCISO)?

An external CISO is a named person. A specialist from the Kertos team takes on the information security officer role for you, supports your ISMS, and is available to your management as a point of contact. You know who you are working with, and you can request evidence of their qualifications.

A virtual CISO (vCISO) describes software- and AI-supported guidance without a permanently named person. At Kertos, KAIA, our AI assistant, supports these tasks: KAIA structures your measures, flags what needs attention, and helps you keep your ISMS documentation current.

In both cases, overall responsibility for information security stays with your management.

Which companies is an external CISO right for?

Companies that run an ISO 27001 ISMS and need the role reliably filled, but do not have the volume to justify a full-time hire. Typical triggers are an upcoming certification or recertification, security requirements in an enterprise deal, NIS2, or the departure of the internal contact who held the role.

What does the Kertos external CISO actually do?

They steer the information security process: reviewing scope and requirements, assessing the risk assessment, preparing and facilitating the management review, reviewing ISMS documentation, evaluating measure and training status, preparing and following up audits, assessing security incidents, and reporting to management. We define the exact scope together with you.

What stays with us?

Overall responsibility for information security, decisions on risk, approvals, and the operational implementation of measures stay with you. You appoint an internal contact, the information security coordinator, who organizes input and makes sure recommendations get addressed in your organization. Your external CISO sets the direction and checks whether the measures work.

Do ISO 27001 or NIS2 require an information security officer?

ISO 27001 requires that responsibilities for information security are assigned and communicated clearly. NIS2 obliges management to own and oversee risk management measures. In both cases, a named person for information security is the usual way to meet that requirement with evidence, and auditors and customers ask for it.

How does the collaboration with the external CISO work?

Remotely, through regular check-ins and ad-hoc coordination as needed. The substance follows the relevant milestones in the ISMS lifecycle: regular risk assessments, management reviews, and upcoming audits. Beyond that, your external CISO supports you as things come up, whether changes, security incidents, or questions from outside parties. The service requires your ISMS to be run in the Kertos platform with the ISO 27001 module.

Any more questions?

Our team is happy to assist you with any questions about our platform, various frameworks, and your compliance needs.

Ask now

📅 Schedule Your 5min Compliance Check

Please enter your business email to continue. We require a company email address to ensure we can best serve your organization.

📞 5min Compliance Check