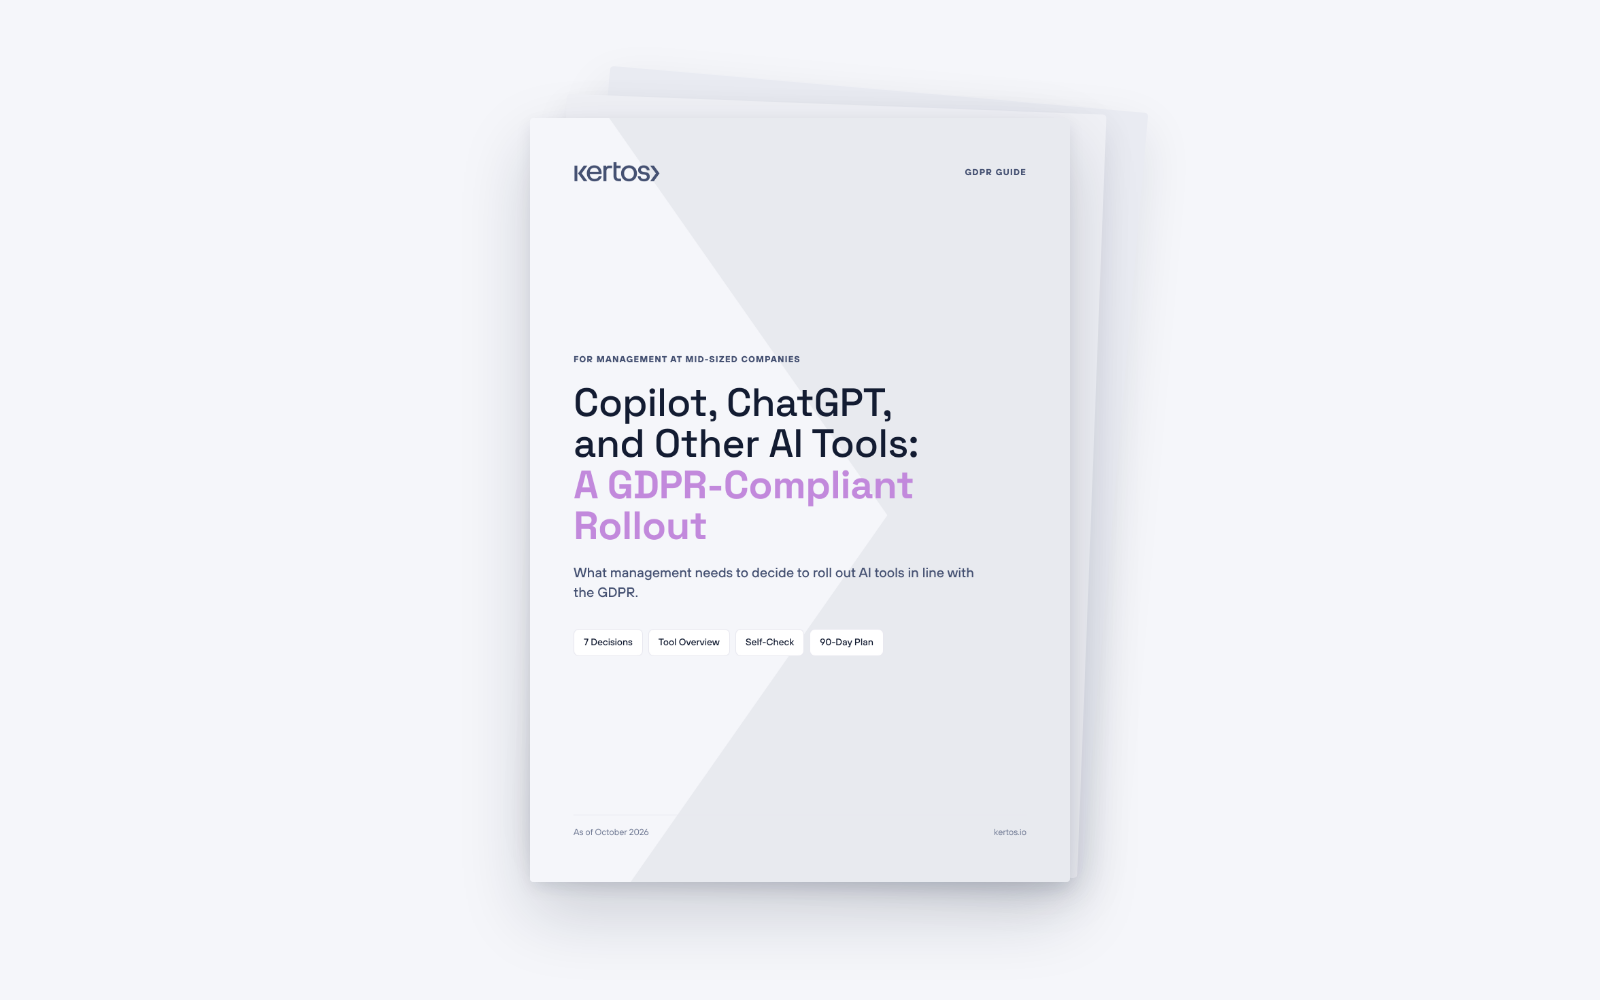
Many employees already use AI tools, often with personal accounts. Under the GDPR, the company remains responsible. This 18-page guide shows management what to decide before approving Copilot, ChatGPT, Gemini, or DeepL:
- The situation: how widely European companies use AI, and why personal accounts are a data protection problem
- Liability: GDPR fines, damages claims, and the duties under the EU AI Act
- The seven decisions for management, from the list of approved tools, licenses, and DPIAs to employee representatives and an AI policy
- A tool overview of Copilot, ChatGPT, Gemini, and DeepL covering licenses, contracts, data location, and pitfalls
- A ten-question self-check that shows where your company stands today
- A 90-day rollout plan in three phases
Every statement is backed by a source and reflects the state of October 2026.
Ready, your compliance to put on autopilot?