
Every company that works with Kertos starts from the same foundation and then makes one important decision: how much managed compliance it wants. Some teams already have a security lead or a data protection officer and want the strongest possible engine behind them. Others want certified experts working next to them on the way to their first audit. Some prefer to hand over the seat entirely, with an appointed external CISO or DPO from Kertos running the program on their behalf.
This article explains how that choice works in practice, for both information security and data protection. It also looks further ahead, because the way European companies buy compliance is changing. The three ways of working with Kertos are an early picture of a service category we believe will shape the next decade of security and privacy work.
What stays the same, no matter how you work with Kertos
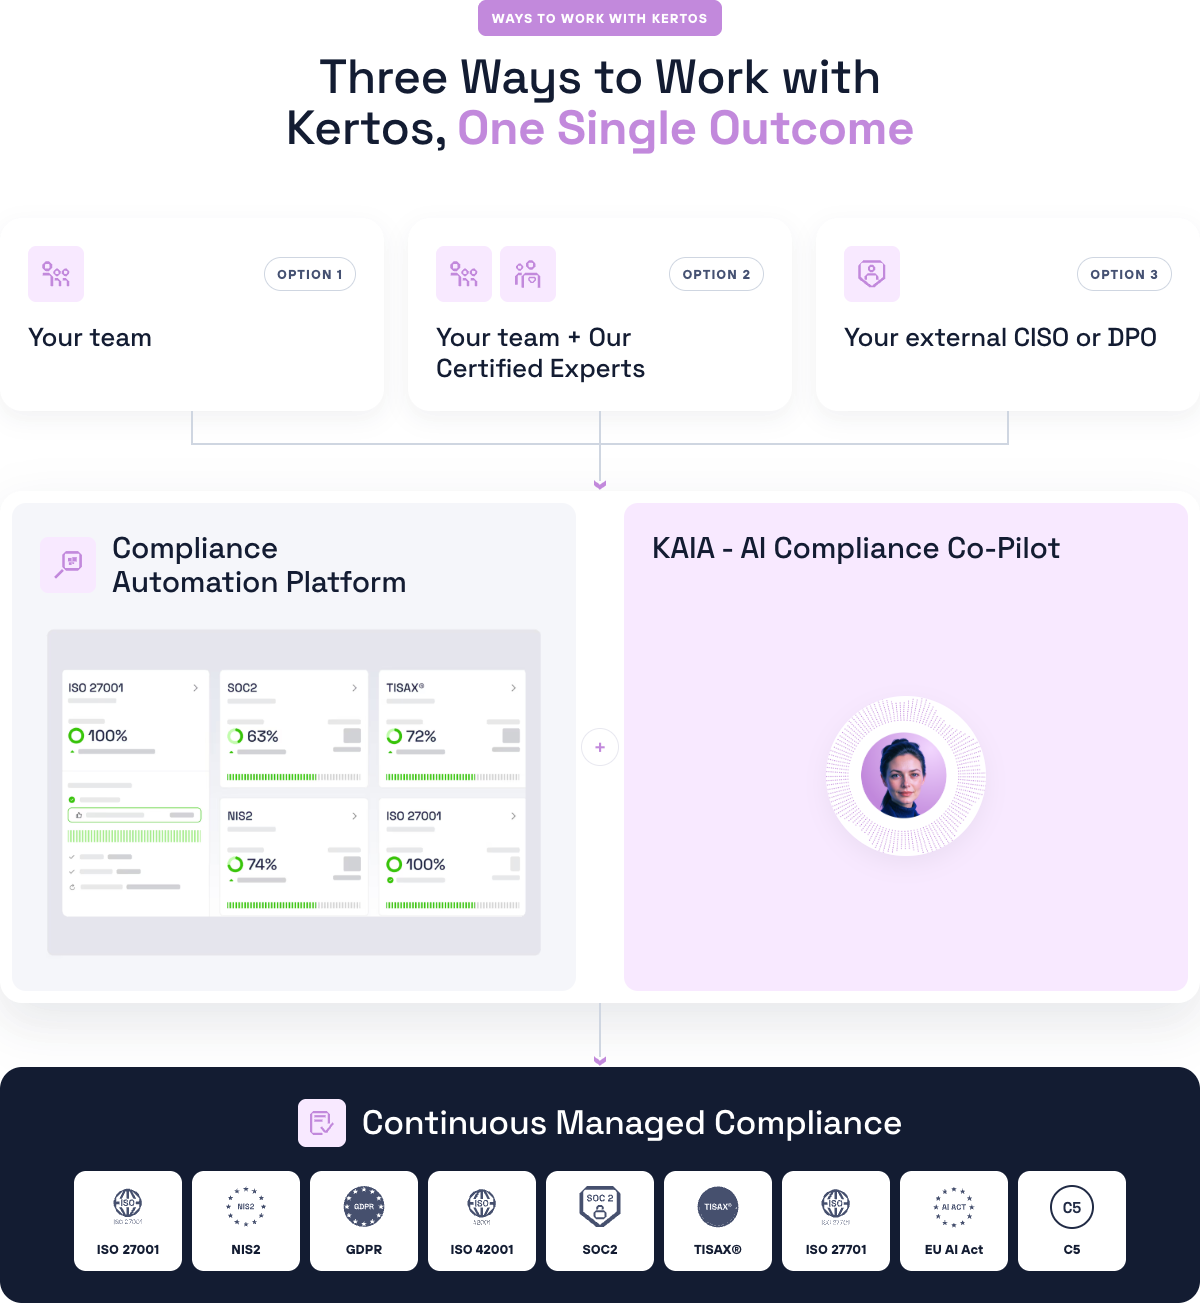
Every Kertos customer works on the same platform with the same foundation. The only thing that changes between the three options is how personally involved our certified experts are, and how much responsibility for the day-to-day work they take on.
At the center of that foundation is KAIA, our agentic AI. KAIA acts as a virtual CISO and a data privacy co-pilot inside the agentic compliance platform. It drafts policies, maps controls across frameworks such as ISO 27001, ISO 42001, NIS2, SOC 2, TISAX and C5, collects evidence from your connected tools, and keeps your records of processing, DPIAs and TOMs current on the privacy side. Every customer also gets onboarding, a Trust Center to share their security posture with customers, and customer success support.
This shared foundation has a practical consequence that matters more than it first appears. Moving from one level of involvement to another never means migrating to a new system. Your controls, your evidence, your risk register and your history stay exactly where they are. The only thing that changes is who is sitting next to you, and how much of the work they carry. Each option builds on the one before it, and you can move up whenever your situation changes.
The three ways to work with Kertos
Think of the three options as a dial of involvement. At one end, your team leads and Kertos equips. In the middle, certified experts work alongside your team. At the other end, Kertos takes over day-to-day ownership through an appointed external CISO or DPO, while your leadership keeps the final say.
Option 1: Your team leads, Kertos equips
This is the right fit for companies that already have compliance expertise in-house: an internal CISO, an information security manager, or an internal DPO. These people own the program. Kertos gives them the engine. A guided kick-off and onboarding get the platform set up, and customer success support helps with every question about how to get the most out of it.
The value here lies in time. An experienced security lead knows what the requirements of the standard itself ask for. What usually slows them down is the manual work around it: chasing evidence, updating spreadsheets, rewriting policies for a second framework. KAIA takes on that routine work, so your in-house expert spends their time on judgment calls.
For data protection, the logic is the same. Kertos becomes the accelerator for your internal DPO, with KAIA handling much of the documentation work that otherwise eats into their week. Compliance decisions, interpretation and ownership stay fully with your people.
Option 2: Certified experts at your side
The second option adds people. Alongside the platform and KAIA, you get access to Kertos certified experts who work with your team from implementation all the way through the audit.
On the information security side, your team still owns the program, and the certified experts act as the colleagues you can call when it matters. They answer questions as they come up, review your approach before the auditor arrives, support you if a security incident happens, and report back on where your program stands. For a company preparing its first ISO 27001 certification, this often makes the difference between guessing at what an auditor expects and knowing it.
On the data protection side, this option goes a step further. Kertos appoints an external data protection officer who takes over your GDPR duties. That includes reviewing data processing agreements, acting as your point of contact with the supervisory authority, supporting you through a data breach, and reporting on the state of your privacy program. Appointing an external DPO is a recognized model, and the regulation explicitly allows it under Article 37(6), where the DPO may fulfill the role on the basis of a service contract.
Many growing companies choose this route for a simple reason. The internal candidates for a DPO role are often the CTO, the head of HR or a managing director, and their existing responsibilities can create a conflict of interest with the DPO's independent role.
Option 3: Kertos takes the lead
The third option is the closest to full ownership. For information security, Kertos appoints an external CISO who manages your compliance for you. This certified expert directs the day-to-day running of your ISMS, prepares risk decisions, gives strategic guidance on where the program should go next, leads you through audit preparation and manages the response if an incident occurs.
For data protection, your external DPO moves from handling duties to proactive support. This option is designed for sensitive data environments, such as health data, large volumes of employee data or complex international data flows. Your DPO stays in regular contact with your team, brings strategic advice to the table and flags risks before they reach you.
An important point of honesty belongs here. Even at this level, your company keeps its accountability. European regulation is clear on this. The NIS2 Directive, for example, requires management bodies to approve cybersecurity risk-management measures and oversee their implementation. Your external CISO or DPO carries the operational load and advises your leadership, and your leadership still makes the decisions and provides the access and context your certified expert needs. If you are in scope for NIS2 compliance, this shared responsibility model is exactly what the law expects.
Comparing the three options at a glance
The table below summarizes how responsibility shifts across the three options. The platform and KAIA are identical in all of them.
How to choose the right level of managed compliance
The right level depends on who you already have in-house, how much time those people really have, and how much ownership you want to hand over. A few honest questions usually settle it.
- Who owns compliance today? If you have an experienced CISO or DPO with time to spare, the first option gives them the strongest support. If nobody owns it yet, or the owner is a founder or CTO doing it on the side, look at the second or third option.
- How much capacity does that person really have? A security lead who is also running IT operations will feel the pressure during audit season. Certified experts at their side take that pressure off.
- How sensitive is your data? Companies processing health data, financial data or large amounts of personal data benefit from a DPO who looks ahead. The official guidelines on data protection officers also explain why independence and the absence of conflicts of interest matter so much for this role.
- What is coming next? A first enterprise customer asking for a certificate, a second framework, a new regulation that puts you in scope. Plan for the level you will need once those changes arrive, then grow into it.
- Remember that the dial moves. Because each option builds on the previous one, you can start where you are today and move up as your company grows, without switching tools or losing your history.
From software to outcomes: where managed compliance is heading
The three ways of working with Kertos are one expression of a bigger shift. Companies increasingly want to buy the result, being compliant and staying compliant, and they want one accountable partner who delivers it. That idea has a name, and we explain it in depth in our guide to compliance as a service.
For most of the last decade, companies had two familiar paths. They could buy compliance software and run it with their own people, which made the work faster while leaving the execution with them. Or they could hire consultants by the hour, who brought valuable expertise to a single audit project and then moved on, taking much of the knowledge with them. Both paths left the customer carrying the risk of whether compliance actually held up over time.
Compliance as a service combines an agentic platform with certified experts and makes the provider responsible for the outcome. The question a company asks changes as a result. It moves from "which tool should we buy" to "how much of our compliance do we want to own ourselves, and how much do we want a partner to own for us?" The three options at Kertos are our answer to that question, expressed as a simple dial of involvement.
We expect the balance inside that model to keep shifting. KAIA already handles a growing share of the routine work, and that share will keep growing: mapping new regulatory requirements as they appear, checking cloud configurations continuously, completing security questionnaires and keeping evidence fresh. As the machine takes on more of the repetitive tasks, the time of our certified experts moves to the work that needs a human: risk decisions, audit strategy, conversations with management and with supervisory authorities.
This changes what compliance feels like for the companies we work with. It becomes an always-on state that runs quietly in the background of the business, through every audit cycle and every new requirement. Your people stay focused on building the company. Your leadership keeps visibility and control. And you know, every day, that your certifications and your GDPR obligations are in good hands. That is the meaning of continuous compliance, and it is the direction managed compliance is taking across Europe.
Frequently asked questions
Can we change how we work with Kertos later?
Yes. Each option builds on the previous one, and every customer uses the same platform. Moving to a higher level of involvement adds certified experts or an appointed external CISO or DPO, while your data, controls and evidence stay where they are.
Does an external CISO or DPO take over our legal responsibility?
Your company and its leadership remain accountable under GDPR and NIS2. An appointed external CISO or DPO from Kertos carries the operational work, advises your management and represents your privacy program toward authorities where the role requires it. Your leadership keeps the final decisions.
Which frameworks does Kertos cover?
For information security, Kertos supports ISO 27001, ISO 42001, NIS2, SOC 2, TISAX and C5. For data protection, Kertos covers ISO 27701 and GDPR compliance, including records of processing, DPIAs and TOMs. Many customers run several frameworks in parallel on the same platform.
Do we still need internal resources if Kertos takes the lead?
Yes, though far fewer. Someone on your side needs to provide access to systems, share context about how your business works and make the decisions that only management can make. Compliance is serious work, and the best results come when your team and your certified experts work on it together.
Where should a company new to compliance start?
Most companies preparing for their first certification start with certified experts at their side or with an appointed external CISO, because guidance during implementation saves time and uncertainty before the audit. The easiest way to find your starting point is a conversation with our team.
Find the level that fits your team
The right way to work with a compliance partner is the one that fits your team, your data and your plans for the year ahead. Whether you want an engine for your in-house expert, certified experts at your side or an external CISO who runs the program for you, the platform underneath stays the same, and the goal stays the same: continuous compliance and the peace of mind that comes with it. If you want to find out which level fits you, book a conversation with a Kertos certified expert and we will map the path from where you are today to your next audit.